Tech
Binance Finance: Internet Heists and TraderTraitor
Most computer whizzes and hacktivists are not as interesting as they make themselves out to be. Before they decided to make money and abandon any pretext to a sound philosophy about civic duty, they at least had the merit of being a useful counterpoint to state secrecy and paranoid officialdom. The focus now is on cash, exchange and systems of faux funny money, with the vultures of government also seeking their spoils. And where there is money, whatever form it takes, there will be robbers, ever watchful over the next heist.
Binance, the world’s largest cryptocurrency exchange boasting over 300 million globally registered users, has found itself in a huge spot of bother with a hack worth $6.3 billion that took place on October 29 in a 20-minute spell starting at 20:05 UTC. Binance wallets on ten blockchains were the subject of the target. While this field teams with jargon, the notable blockchain analytics firm TRM Labs offers some instructive information on this feat of digital plunder: “Within minutes, Binance wallets on the XRP Ledger, Ethereum, Bitcoin, Tron, Solana and four other networks had sent their balances to addresses controlled by a single attacker.” A second wave took place at 23:05 UTC, targeting Binance wallets on Avalanche and Polygon.
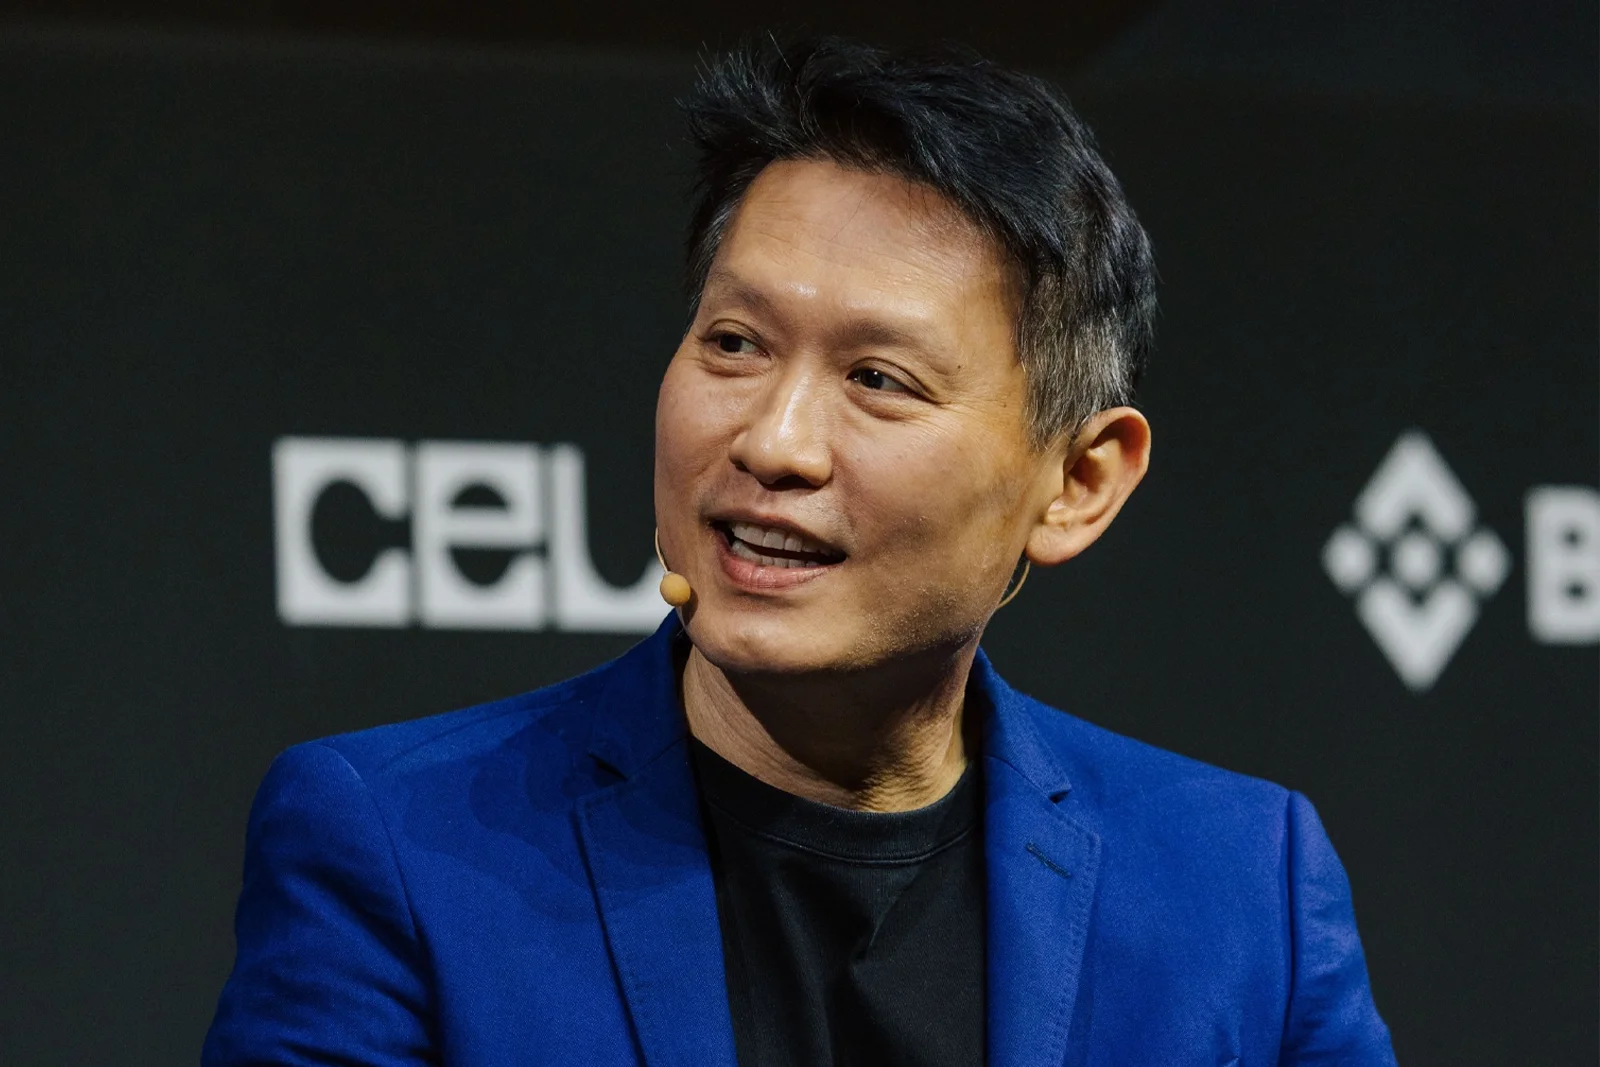
This passes, by an impressive margin, the Bybit exchange hack in 2025, worth $1.5 billion. Initial suspicion fell on a compromised engineer’s laptop. In time, it became clear that there were more areas of vulnerability; according to the company’s own description, there were “additional points of breach.” Binance co-CEO Richard Teng insists that “the attacker did not simply use one engineer’s permissions, and this was not a single ‘one-click’ action. It involved a more complex attack process.”
Another of the company’s co-chief executives, Yi He, thanked cryptocurrency issuers for a brisk freezing of assets. “Safety first: withdrawals are currently disabled until the environment is confirmed to be secure.” Binance’s own SAFU fund is set to cover most of the losses (95% so far), while jumpy customers took out more than $3.6 billion after the exchange opened on November 1. The company executives are keen to stress that the target was the company’s hot wallet, not customer funds, using an EIP-7702 delegation to seize control. The company generally keeps most of its user assets in cold wallets, only moving them to hot wallets when withdrawals are sought.
The U.S. Federal Bureau of Investigation has found what it claims to be the culprit: North Korea’s TraderTraitor outfit. The FBI claims to have observed hackers converting the pilfered assets into Ethereum, a cryptocurrency that will be converted again through means of decentralised finance (DeFi) and instant swap services. The Bureau has urged those in the virtual asset business “to block transactions with or derived from addresses TraderTraitor actors are using to launder these stolen assets.” The cyber activities of North Korea, specifically directed at cryptocurrency companies, have certainly caught the eye of a panel of UN experts who report to the Security Council. In March 2024, the panel revealed it was looking at 58 such suspected cyber-attacks conducted by the DPRK between 2017 and 2023 worth $3 billion “which reportedly help to fund the country’s development of weapons of mass destruction.”
Chainalysis and TRM Labs have also identified TraderTraitor as responsible for the misdeeds against Binance, an outfit which also goes by the more benign name of the Lazarus Group. “Several features of this match earlier North Korea-linked heists,” TRM Labs suggested in a statement, “including the Bybit hack [in February 2025] and the KelpDAO hack in April 2026: small Tornado Cash withdrawals funding an operator wallet, staging that began well before the theft, and signatures obtained in advance then executed in one burst.” The advantage for those using the service known as Tornado Cash is that it occludes the origins of the crypto.
The initial question for Binance must surely be why a single employee’s laptop computer had access to systems spanning billions of dollars in funds. But given the company’s own statements that the attacks took place at other points, we must assume a broader fragility with the security systems in play. The edifice seemed a most porous one. As Pieter Arntz of the cybersecurity firm Malwarebytes puts it, “The real question is what allowed that initial foothold to become access to withdrawal systems – and which safeguards failed to stop unauthorized access.”
The cryptocurrency lobby is perennially allergic to government regulation, a sentiment not entirely without good cause or sense. But when platforms reach a stage where billions of holders’ money is at stake, financial regulators and other agencies will have some grounds to intervene. Attacks of this sort also precipitate the prospect of further fraud and deception in the markets, with the distribution of malicious links to lure the unsuspecting customer.
But the optimists remain bushy-tailed about the theft in terms of global financial stability. Feike Hacquebord, who is a boffin on threat research at TrendAI, is of the view that approximately half of the stolen funds were already frozen, “while the regulated banking system is well equipped to absorb the shock of this size. This is a major crisis for Binance, not a crisis for the global financial system.” Why should we not be reassured?